Source · Firecrawl · Verified November 1, 2026

Firecrawl
Short answer: Firecrawl lifecycle webhooks report crawl, batch scrape, extract, agent and monitor progress with page-level results.
Hooks verifies Firecrawl deliveries with hmac-sha256, lowercase hex, sha256= prefix over the raw body and normalizes them into the unified event format.
Set up the webhook in Firecrawl
- Create a crawl, batch scrape, extract, agent or monitor with a
webhookobject that points at your Hooks receive URL. - Copy the account webhook secret from Firecrawl → Settings → Advanced into the Hooks source secret field; Firecrawl sends
X-Firecrawl-Signature: sha256=<hex>over the raw body. - Keep the default event list or subscribe to a subset. Retries at 1, 5 and 15 minutes reuse the same webhookId, so Hooks dedupes exact retries; the Firecrawl job id is never used as the delivery id.
Signature verification
| Header | X-Firecrawl-Signature |
|---|---|
| Algorithm | HMAC-SHA256, lowercase hex, sha256= prefix over the raw body |
| Replay window | none |
| Delivery id | Body `webhookId` |
Events Hooks normalizes
| event.type | subject | What it means |
|---|---|---|
crawl.page | event | Firecrawl lifecycle webhooks report crawl, batch scrape, extract, agent and monitor progress with page-level results. |
Normalized payload
Every adapter produces this shape before filters or templates run. The raw payload and sanitized headers stay attached for audit, but filters and templates read the normalized fields.
Normalized event
{
  "id": "evt_demo",
  "source": "firecrawl",
  "type": "crawl.page",
  "action": "page",
  "deliveryId": "delivery_demo",
  "subject": {
    "title": "Firecrawl event"
  },
  "raw": {
    "success": true,
    "type": "crawl.page",
    "id": "019c2c3f-7d4e-7a11-9b3c-2f6d1e8a4c90",
    "webhookId": "019c2c40-1a2b-7c3d-8e4f-5a6b7c8d9e0f",
    "data": [
      {
        "markdown": "# Example page",
        "metadata": {
          "title": "Example page",
          "url": "https://example.com/pricing",
          "statusCode": 200,
          "scrapeId": "019c2c41-2b3c-7d4e-8f5a-6b7c8d9e0f1a"
        }
      }
    ],
    "metadata": {
      "environment": "production"
    }
  }
}
Filter and template examples
Filter
type equals "crawl.page"Template
"Firecrawl event: {{event.subject.title}}"Retries and the delivery log
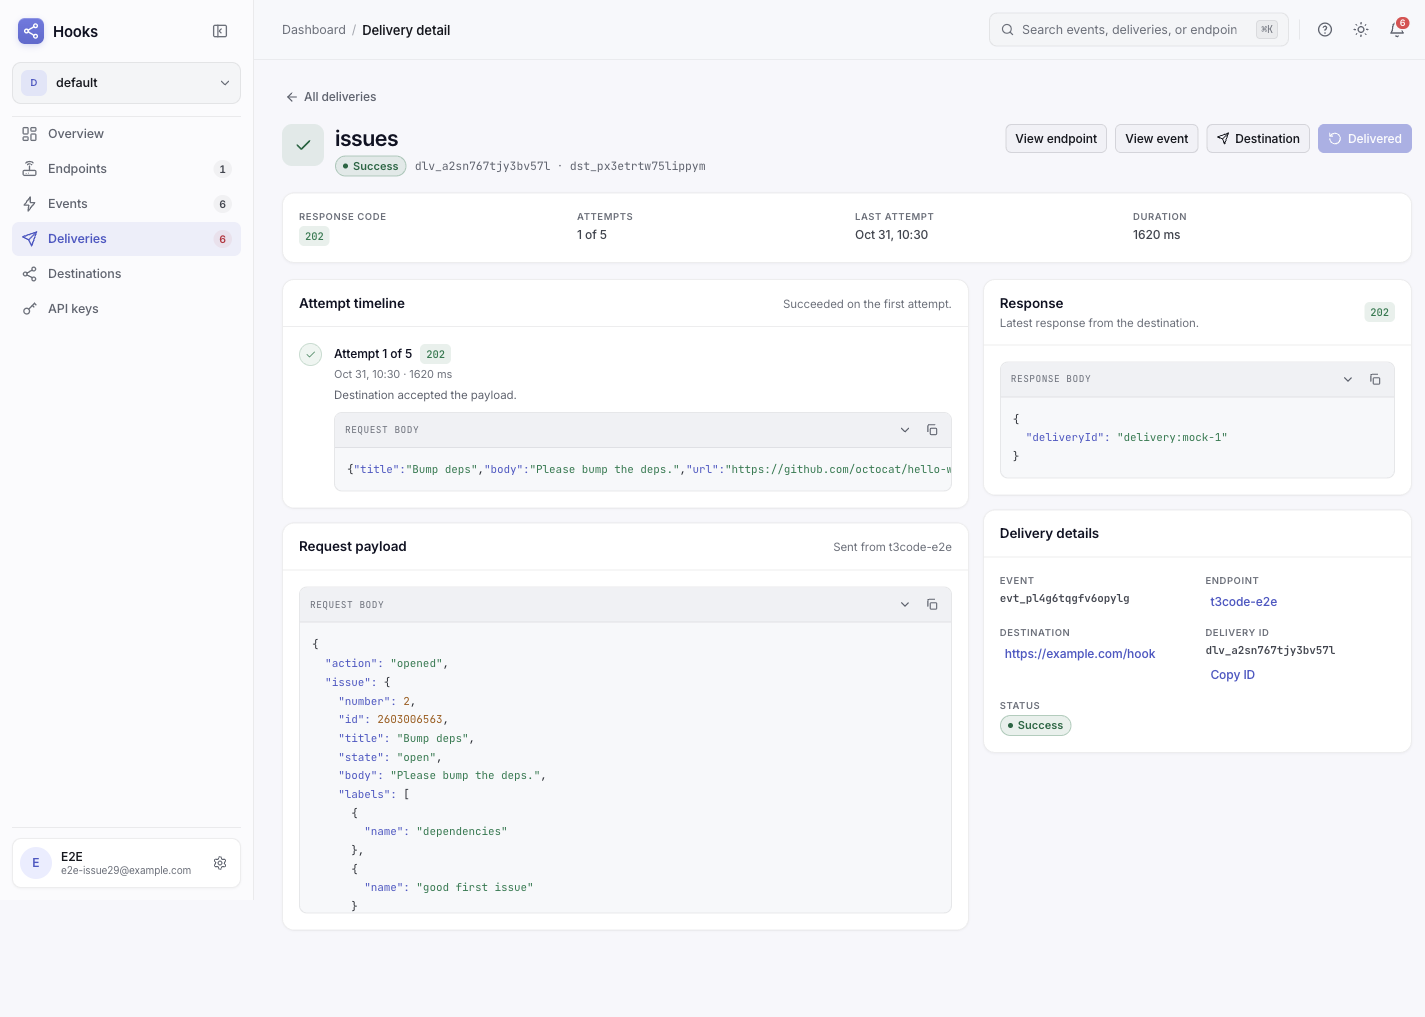
408, 425, 429, and 5xx responses retry with backoff and honor Retry-After; other 4xx responses fail permanently with a named code. Every attempt keeps the rendered request and the target response, so a failure points at one field or one status instead of a guess.
Common errors
| Symptom | Fix |
|---|---|
SIGNATURE_INVALID | Use the signing secret Firecrawl shows when the webhook is created, and send X-Firecrawl-Signature for the exact raw body. |
Nothing arrives | Confirm the webhook points at the endpoint's /in/<endpoint-id> URL and that the endpoint is active. |
Pair with a target
Reference
- Receiving eventshttps://docs.firecrawl.dev/webhooks/events
- Verify signatureshttps://hooks.events/docs/signatures.md
- Payload templateshttps://hooks.events/docs/templates.md
Other sources


X-Hook-Secret handshake.Auth0Auth0 custom log streams POST tenant log events (login, signup, logout, token exchange, user changes) to a webhook.AWS SNSAWS SNS delivers JSON notifications and subscription confirmations to HTTP(S) endpoints, signed with an RSA certificate published under an sns.<region>.amazonaws.com URL.Azure DevOpsAzure DevOps service hooks send git pushes, pull requests, work items, builds and releases to a public webhook endpoint.BitbucketBitbucket Cloud repository webhooks cover pushes, pull request changes, and issue events.BrowserbaseBrowserbase Functions webhooks report invocation and build lifecycle states (pending, running, completed, failed).Cal.comCal.com booking webhooks wrap the booking in a 


triggerEvent envelope and sign each delivery with an HMAC-SHA256 of the raw body.Browse all sourcesSetup steps, signatures, events, and payload samples for every provider.