Guide · Stripe → Lark · Verified November 1, 2026
Stripe to Lark webhook guide
Short answer: One Stripe endpoint verifies each delivery, a destination filter keeps the events in this guide, and every match is delivered to Lark with its own retry schedule and delivery log.
The finance group tracks revenue in Lark. This pairing posts each paid invoice into the group with the amount and the invoice link, and signs the request when the bot's signature check is enabled — the common setup for a group that also receives other bots.
At a glance
id when it starts with evt_, stable across Stripe retries.Target: LarkA Hooks Lark destination posts a text message to a group's custom bot webhook on open.larksuite.com. The URL is a project secret, and when the bot's signature check is on, Hooks adds the timestamp and HMAC-SHA256 signature the bot requires.1. Configure the Stripe webhook
- In the Stripe Dashboard, open Developers → Webhooks → Add endpoint.
- Paste the endpoint's ingestion URL and select the events you need (invoice, checkout, subscription).
- Copy the endpoint's Signing secret (`whsec_...`) into the Hooks endpoint secret.
- Send a test event from the Stripe Dashboard and confirm it in the delivery log.
HMAC-SHA256 over <t>.<raw body>; any matching v1 signature passes. Five minutes between t and the current time.
2. Filter to the events that matter
Filters run per destination before rendering, so a non-matching event is stored with no delivery and no agent call. The rules below are the difference between a useful pairing and a noisy one.
Filter: paid invoices only
{
  "allow": [
    { "field": "event.type", "op": "equals", "value": "invoice.paid" }
  ]
}
3. Configure the Lark destination
A Hooks Lark destination posts a text message to a group's custom bot webhook on open.larksuite.com. The URL is a project secret, and when the bot's signature check is on, Hooks adds the timestamp and HMAC-SHA256 signature the bot requires.
Destination: Lark custom bot
{
  "webhookUrl": "{{secret.LARK_WEBHOOK_URL}}",
  "text": "Invoice paid: {{event.subject.title}}\n{{event.subject.url}}",
  "signature": { "secret": "{{secret.LARK_SIGN_SECRET}}" }
}
Secrets enter configs only as {{secret.NAME}} references; literal credentials are rejected. Full Lark target guide
4. Verify the delivery and its retries
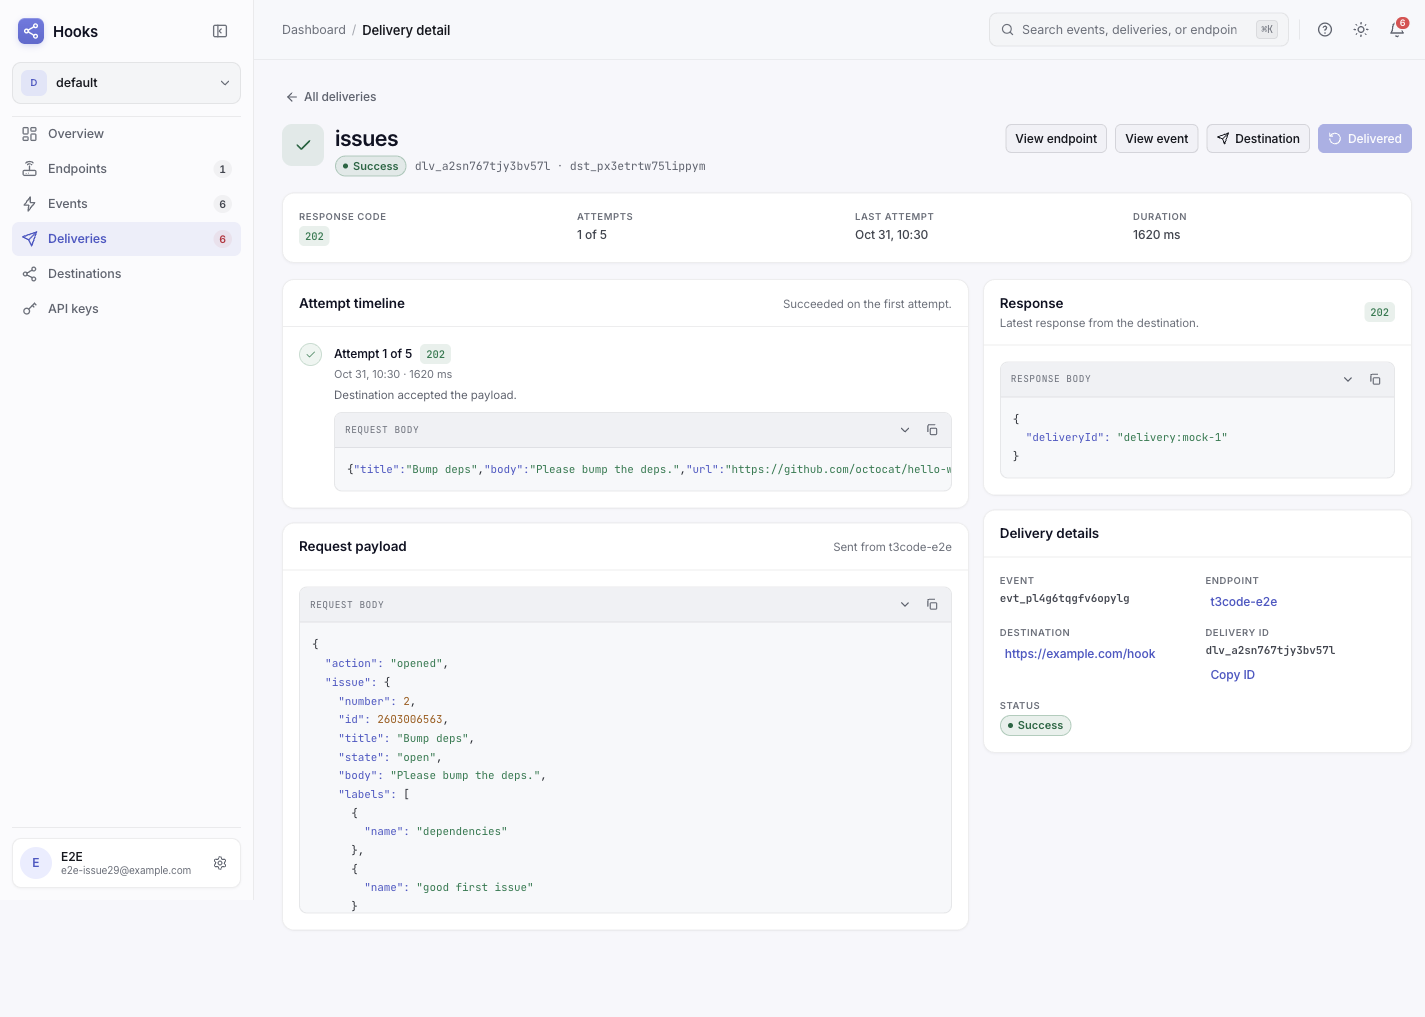
Send one real event from the source, then open Deliveries. A 2xx from the target means accepted, not finished. 408, 425, 429 and 5xx retry with backoff honoring Retry-After; other 4xx fail permanently with a named code. The rendered request is stored per attempt, so a bad field path is visible without re-sending.
The pitfall this pairing hits
Only text messages are built, so cards belong elsewhere. This target renders msg_type: text only. A post or interactive card needs its own JSON body, which the Lark target does not build — send it through a generic webhook destination or the HTTP target instead of forcing card JSON into the text field.
Frequently asked questions
Do I need one endpoint per source or one per destination?
One endpoint per source. Each destination under that endpoint carries its own filter, template, retry schedule, and delivery log, so the same event can feed several targets without duplicate ingress URLs.
What happens while the target is down?
Retryable failures back off and retry within the destination's window; permanent 4xx failures stop immediately. Either way, the original event stays stored, so after fixing the target you replay the event instead of asking the source to send it again.
Only text messages are built, so cards belong elsewhere
This target renders msg_type: text only. A post or interactive card needs its own JSON body, which the Lark target does not build — send it through a generic webhook destination or the HTTP target instead of forcing card JSON into the text field.